An agency, freelancer, or external contractor needs to sign in to your CMS, advertising platform, or client portal. The usual shortcut is to send the password by email or chat. It is fast, but control is lost immediately: the secret can be copied, retained, or forwarded without your knowledge.
A cleaner approach is to share the ability to sign in rather than the password itself. The authorized user finds the account in a browser extension, starts autofill, and accesses the service without displaying or copying the secret.
Why should you avoid sending passwords directly?
A password sent in a conversation often remains in history for months. Even after the assignment ends, it may still exist on a phone, in a mailbox, or in a backup. It also becomes difficult to know who actually has it.
France’s data protection authority recommends limiting the number of people who know a password, reviewing rights regularly, and using a password manager. It also recommends removing permissions when a user is no longer authorized. See the CNIL guidance on user management and access rights.
How connection-only access works
The owner keeps the credential in their vault and selects the recipient’s access level. With connection-only access:
- the recipient cannot reveal the password in the application;
- copying the secret is disabled;
- sign-in is performed by the extension on the intended domain;
- the owner can revoke access at any time;
- the recipient cannot edit or delete the owner’s credential.
This separation is useful when someone needs to use an account without becoming its owner. It does not replace individual accounts offered by some services, but it improves situations where a shared account is still technically required.
A simple five-step process
1. Check whether the service supports individual accounts
Before sharing access, look for a users, members, or roles feature. A named account with only the necessary rights remains preferable. Controlled sharing is mainly for services that only offer a common account or have insufficient role management.
2. Save the correct sign-in address
Associate the credential with the domain that is actually used. The extension can then suggest the right account on the right site and avoid confusion between similar production, staging, and administration interfaces.
3. Choose the recipient and duration
Share only with the person concerned. For a short assignment, record the expected end date from the start. Temporary permission that is never reviewed often becomes permanent.
4. Allow sign-in without password visibility
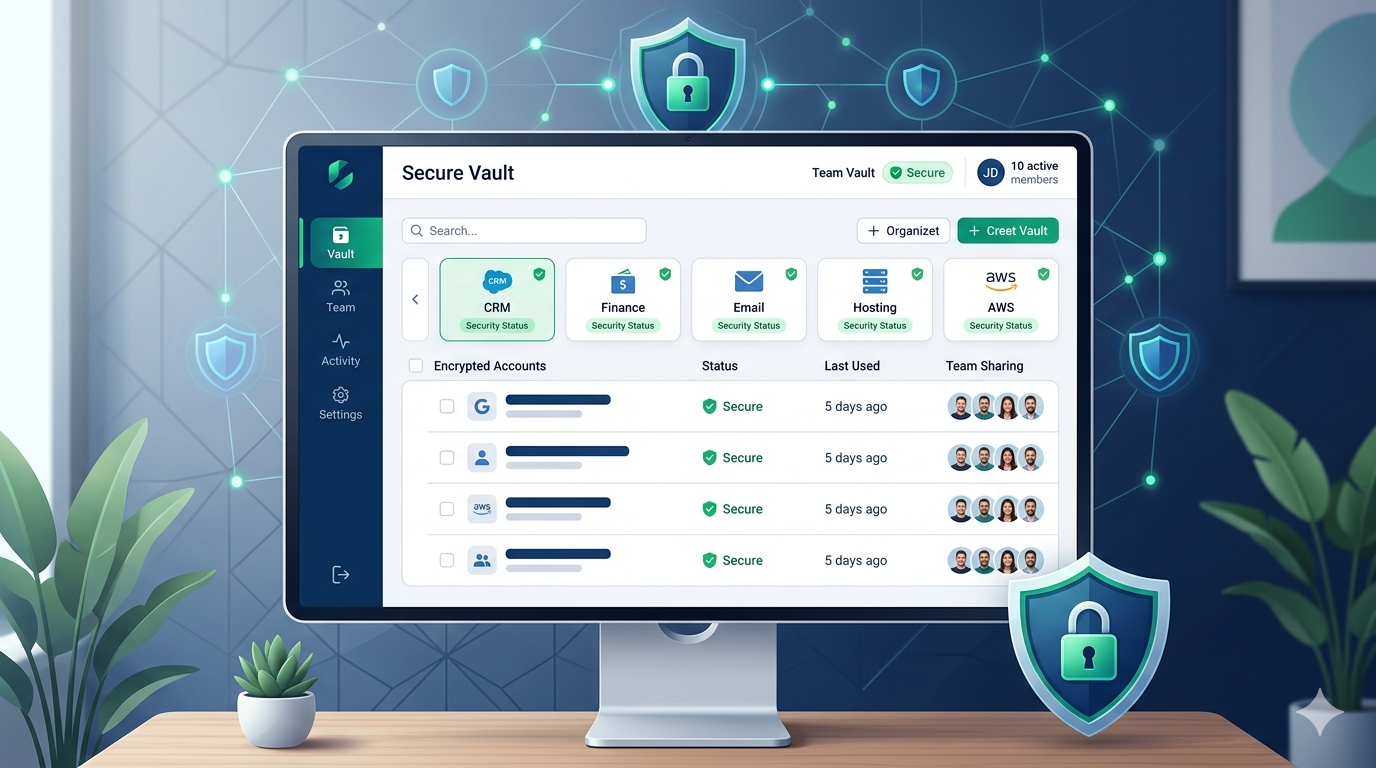
In MYKEYNEST, choose the sharing option that allows use through the extension without permission to view or copy the password. The recipient signs in with their own MYKEYNEST account and selects the authorized credential.
5. Revoke and review access when the assignment ends
Remove the share as soon as the collaboration ends. If the password was previously disclosed or you suspect it was copied, change it on the target service as well.
What are the limitations?
No browser mechanism turns a shared account into an individual account. Once signed in, a person may still be able to change information if the target service grants that permission. For sensitive tools, combine several measures:
- enable multi-factor authentication when available;
- do not share an administrator account for an ordinary task;
- limit access to the required time and scope;
- review the activity history provided by the target service;
- prefer individual accounts whenever the service supports them.
NIST also notes that passwords alone are not phishing-resistant. For critical accounts, prefer strong or phishing-resistant authentication whenever possible. Read the NIST SP 800-63B-4 authentication guidance.
Contractor access checklist
- The need and the access owner are identified.
- An individual account is unavailable or unsuitable.
- Permissions are limited to the assignment.
- The password is not sent in a conversation.
- A review or revocation date is scheduled.
- MFA is enabled on important accounts.
Use this workflow with MYKEYNEST
MYKEYNEST centralizes credentials, sharing with collaborators, and browser-extension autofill. Owners stay in control and can remove permission without searching old conversations for a password.
Explore MYKEYNEST access management or create your free vault.