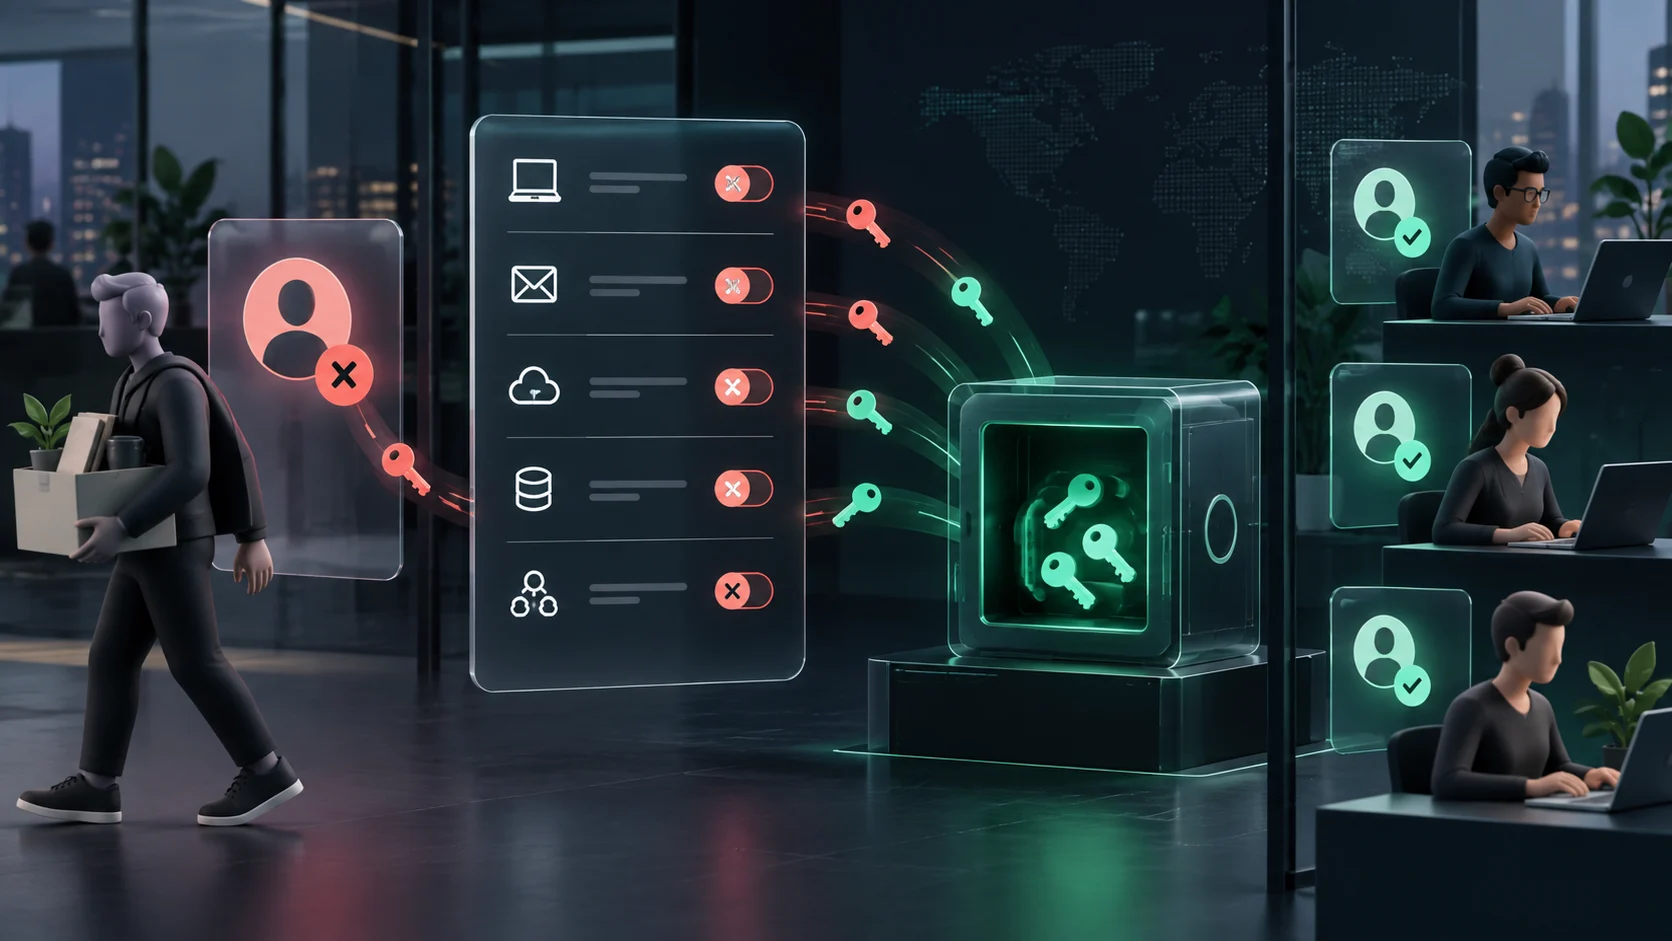
When an employee or contractor leaves the company, returning a laptop is not enough. They may still have access to email, CRM, hosting, social media, online stores, or shared accounts that were never inventoried.
An effective offboarding procedure should be short, assigned to specific owners, and prepared before the final day. The goal is twofold: remove the departing person’s rights without blocking the remaining team.
Why does offboarding leave forgotten access behind?
Permissions accumulate throughout a project. Some are granted directly in an application; others come through a group, shared password, extension, or temporary invitation. Without a central inventory, the person managing the departure has to reconstruct the entire history under time pressure.
ANSSI recommends integrating onboarding, offboarding, and role changes into company procedures and revoking all rights when a person leaves. The CNIL likewise recommends removing permissions as soon as authorization ends and regularly reviewing granted rights.
Prepare revocation before the final day
The manager, HR, and the person responsible for IT should share the same information: end date and time, risk level, equipment to return, and required business continuity. For an administrator or someone with access to sensitive data, the timeline should be especially precise.
Create a list of categories to review:
- email, calendar, and file storage;
- CRM, billing, banking, and business applications;
- CMS, hosting, domains, and code repositories;
- social media, advertising, analytics, and email marketing;
- VPN, Wi-Fi, remote access, and administration consoles;
- password manager, groups, and direct shares;
- devices, hardware keys, badges, and recovery methods.
Checklist for the departure day
1. Disable individual accounts
Suspend or close individual accounts according to the company’s retention rules. Do not blindly delete a mailbox or files containing required information: transfer ownership to an authorized manager first.
2. Remove the person from groups and teams
Disabling an account in one tool does not automatically cancel invitations elsewhere. Review work groups, teams, client spaces, and direct shares.
3. Revoke sessions and devices
Close active sessions and remove associated devices when the service supports it. This matters when the person used a personal device or browser extension.
4. Rotate secrets that were genuinely shared
Change passwords, API keys, or recovery codes that the person may have viewed or copied. Rotating every secret can cause unnecessary disruption; focus on those whose confidentiality is no longer assured.
5. Verify continuity
Confirm that another authorized team member can access essential accounts, receive recovery codes, and administer domains or paid services. No critical account should depend on one person.
What should you do with shared accounts?
A shared account creates two different situations:
- the password was visible: change it and update the vault;
- the person only had controlled access: revoke the share and review active sessions on the target service.
For important services, review MFA as well. An old phone, security key, or recovery code may remain valid even after the password changes.
After departure: verify instead of assuming
During the following days, inspect the logs available on critical services and confirm that invitations are gone. Record who performed each action and when. This evidence prevents duplicated work and makes future reviews easier.
The CNIL access-rights guidance recommends regular reviews, at least annually, to remove unused accounts and align rights with each role. The ANSSI cyber hygiene guide also provides a useful foundation for formal onboarding and offboarding.
A reusable procedure
- Manager or HR initiates the process.
- Access is inventoried automatically or manually.
- The business owner validates the list.
- Revocation occurs at the scheduled time.
- Ownership is transferred and relevant secrets are rotated.
- A final review is completed and the checklist archived.
Centralize sharing with MYKEYNEST
In MYKEYNEST, a credential owner can remove a share without deleting the password for the rest of the team. Groups also prevent administrators from searching for every credential individually when a member’s scope changes.